Company Award
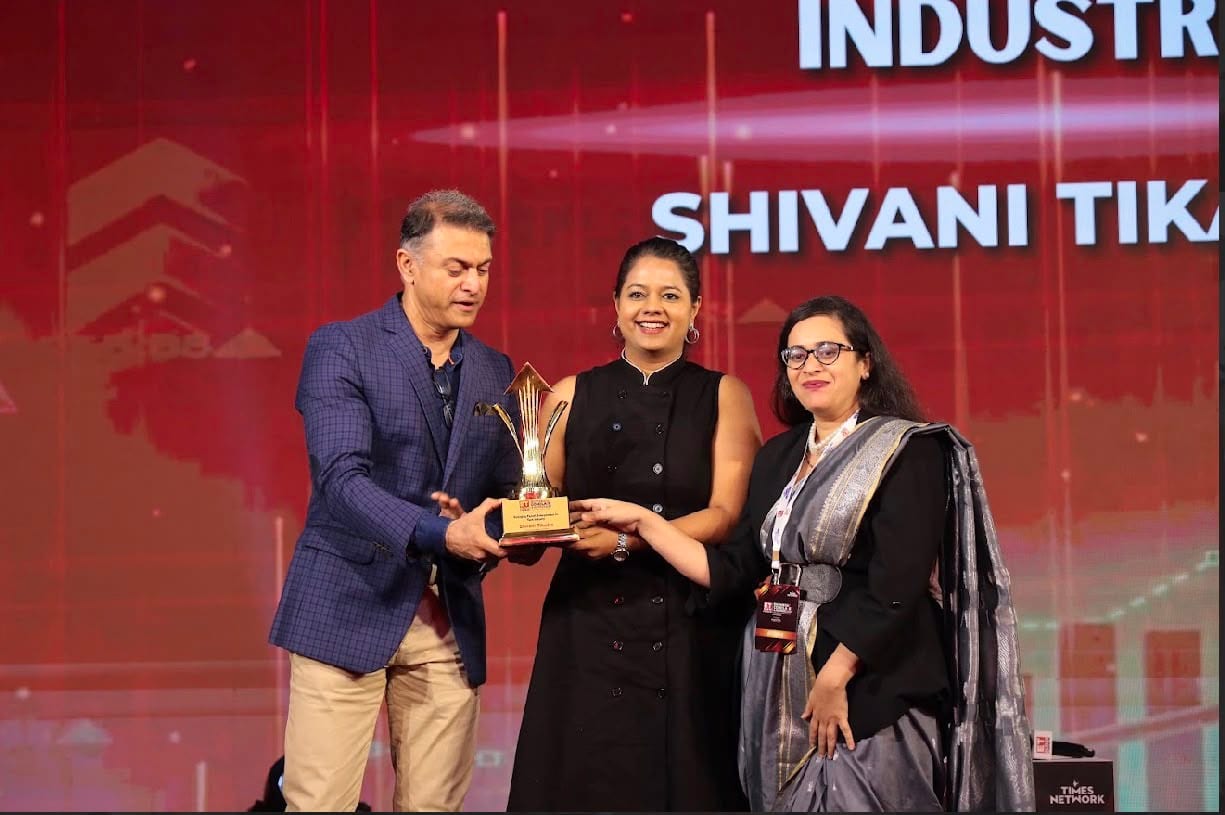
Emerging Tech Start-up of the Year
Recognised for building AI enabled security and compliance services that help growing companies meet the enterprise trust bar.
AI Enabled Security Solutions
Founded by a security leader who believes world-class protection should not be a privilege, but a foundation every ambitious enterprise deserves.
To make world-class security and digital trust accessible to every organization with global ambition, no matter their size or stage.
To simplify the complex: delivering intelligent, end-to-end solutions that let enterprises grow fearlessly, stay resilient, and earn lasting trust.
Integrity, Innovation, Empathy, Excellence, and Accountability guide every engagement we deliver.
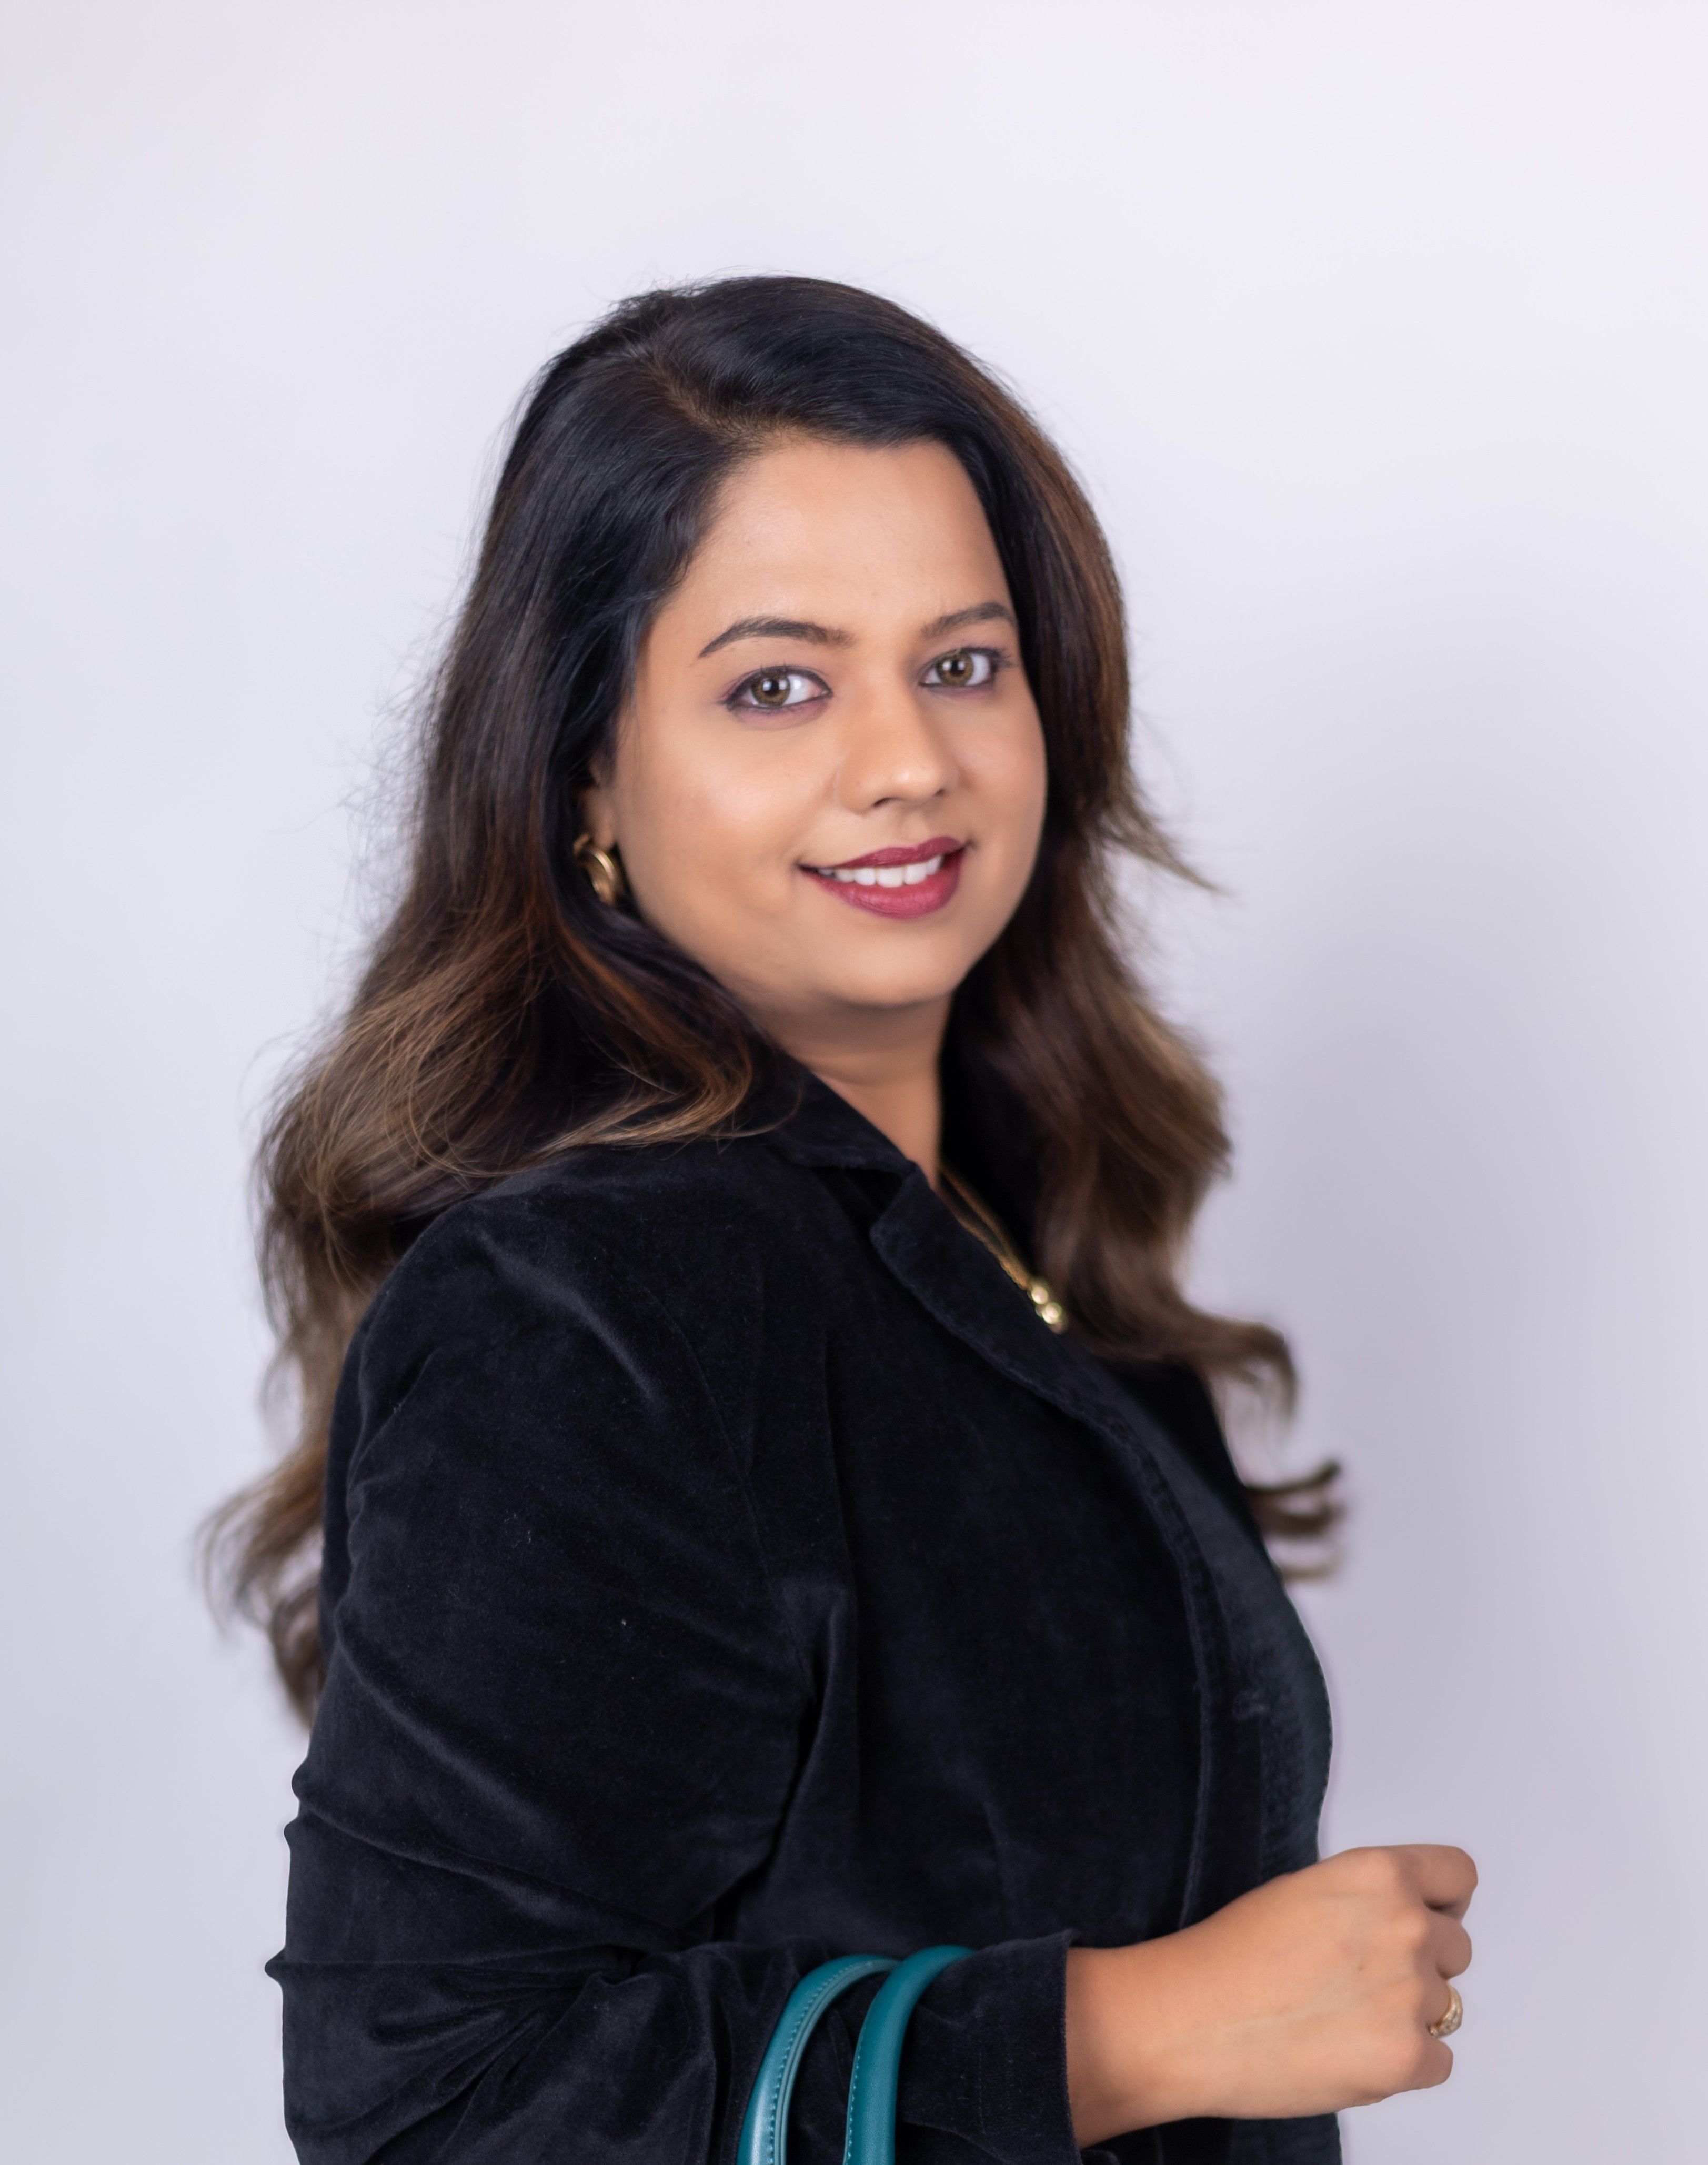
Shivani Tikadia
Ex-PwC. 10+ years of enterprise security leadership. Trusted partner to 50+ Fortune 500 companies.
“Behind every compliance requirement is a business dream. We exist to protect that dream, so visionary teams can move faster, with absolute confidence.”
Over 100 customers across the globe, from global enterprises and fast-scaling unicorns to governments, partner with SecComply to secure what matters most.
…and 80+ more growing organizations across 4 continents.
0+
Clients secured
0+
Audits delivered
“SecComply reduced our SOC 2 audit prep from 12 weeks to just 10 days. The automated evidence collection alone saved us hundreds of hours.”
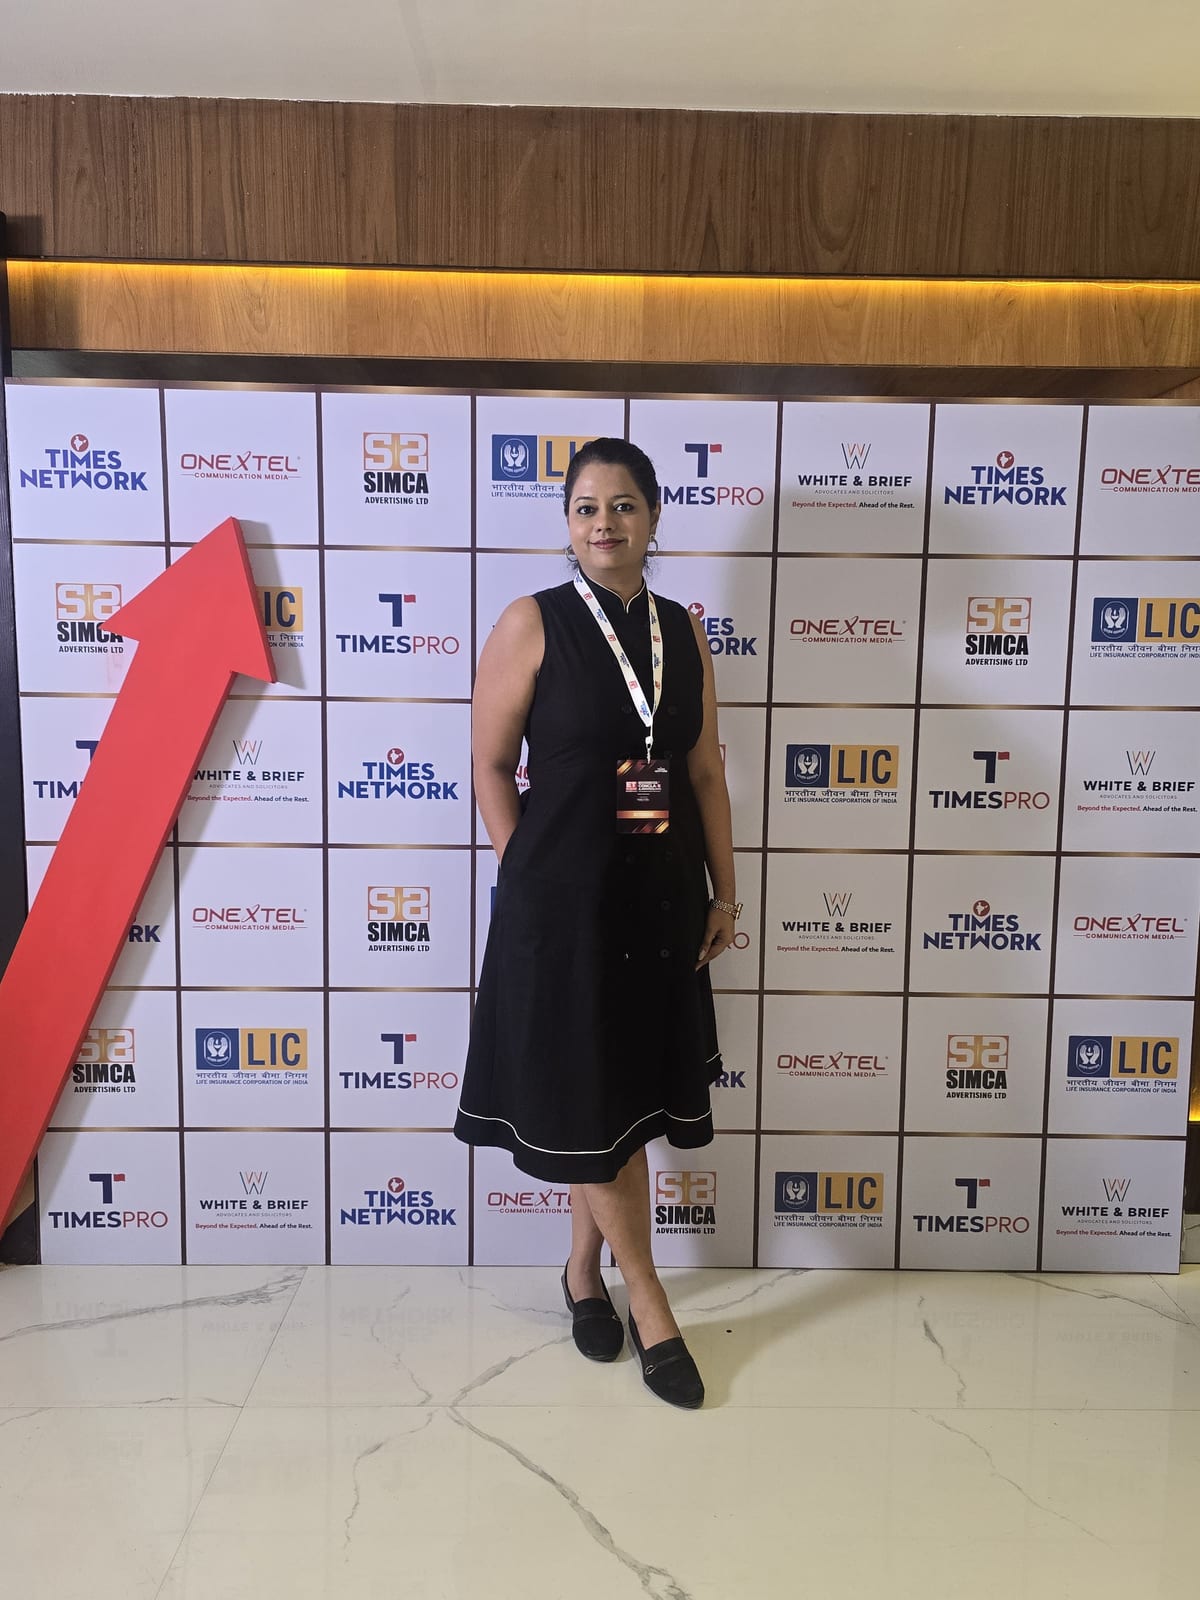
On 25 August 2026, SecComply was honoured at the ETNOW.in Business Conclave & Awards 2026, West Edition, in Mumbai.
Recognised for building AI enabled security and compliance services that help growing companies meet the enterprise trust bar.
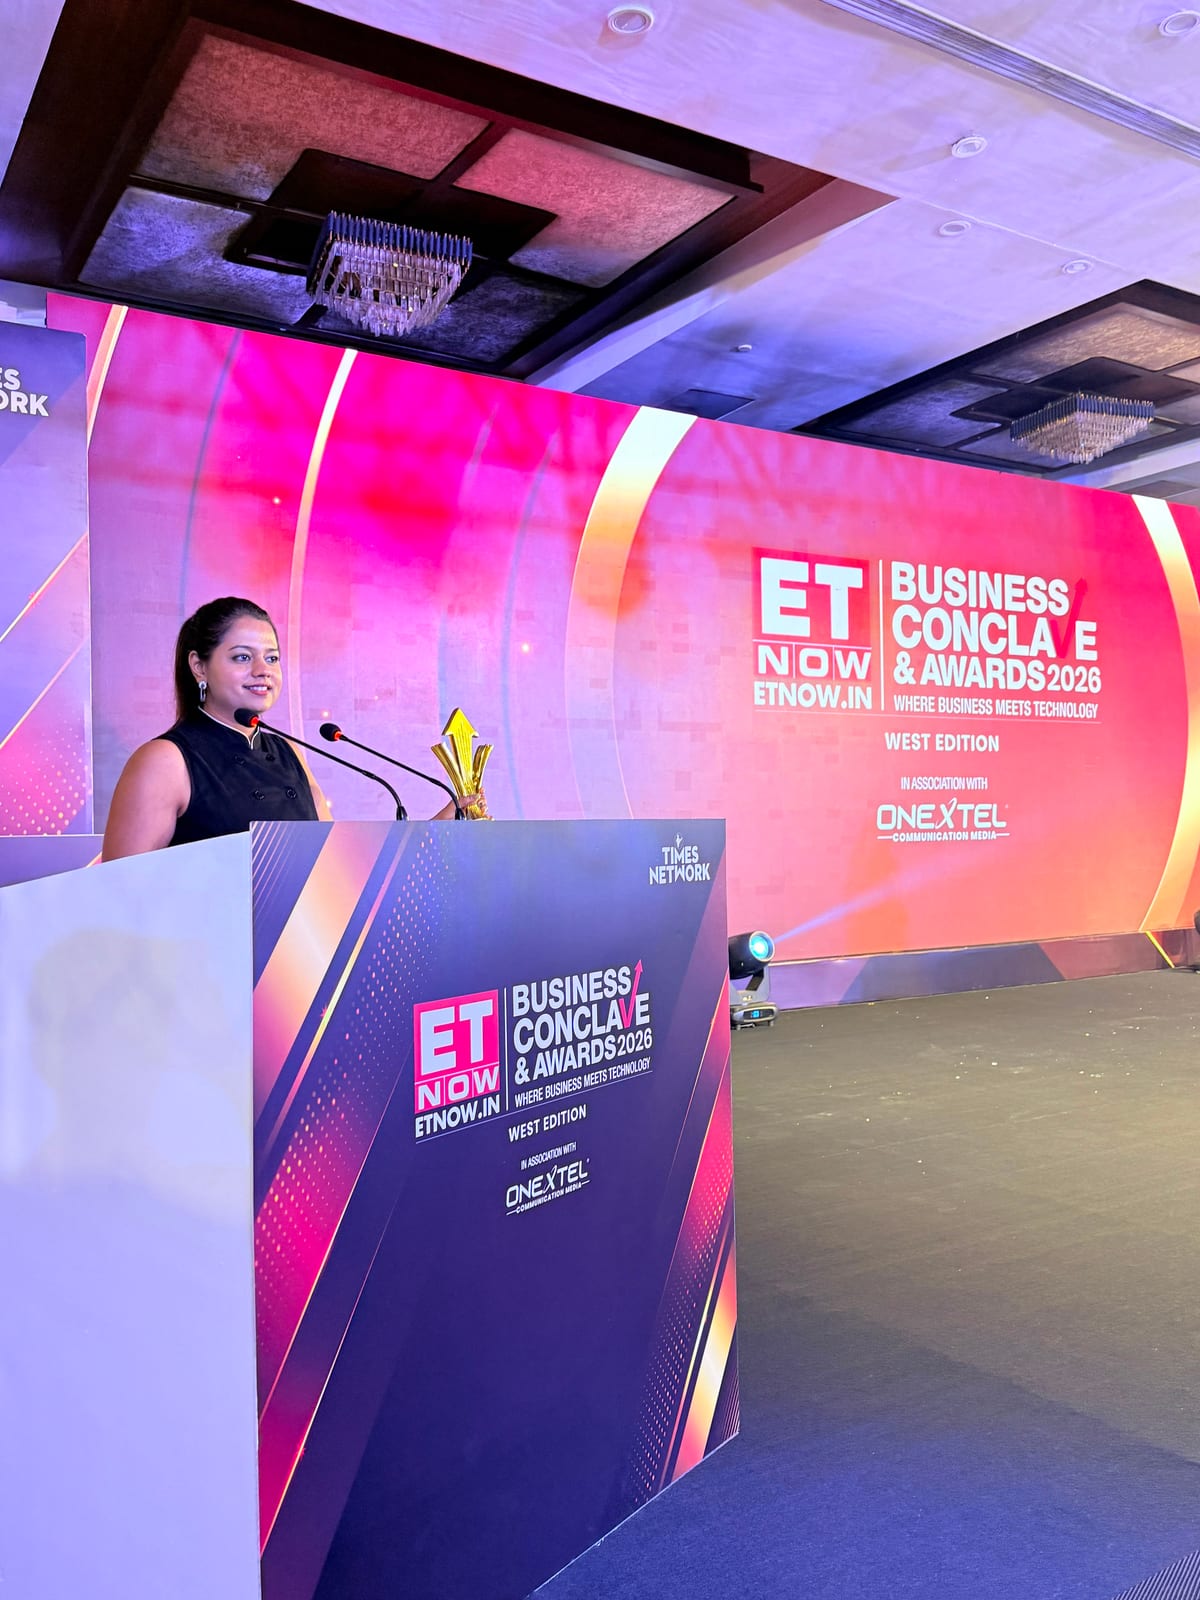
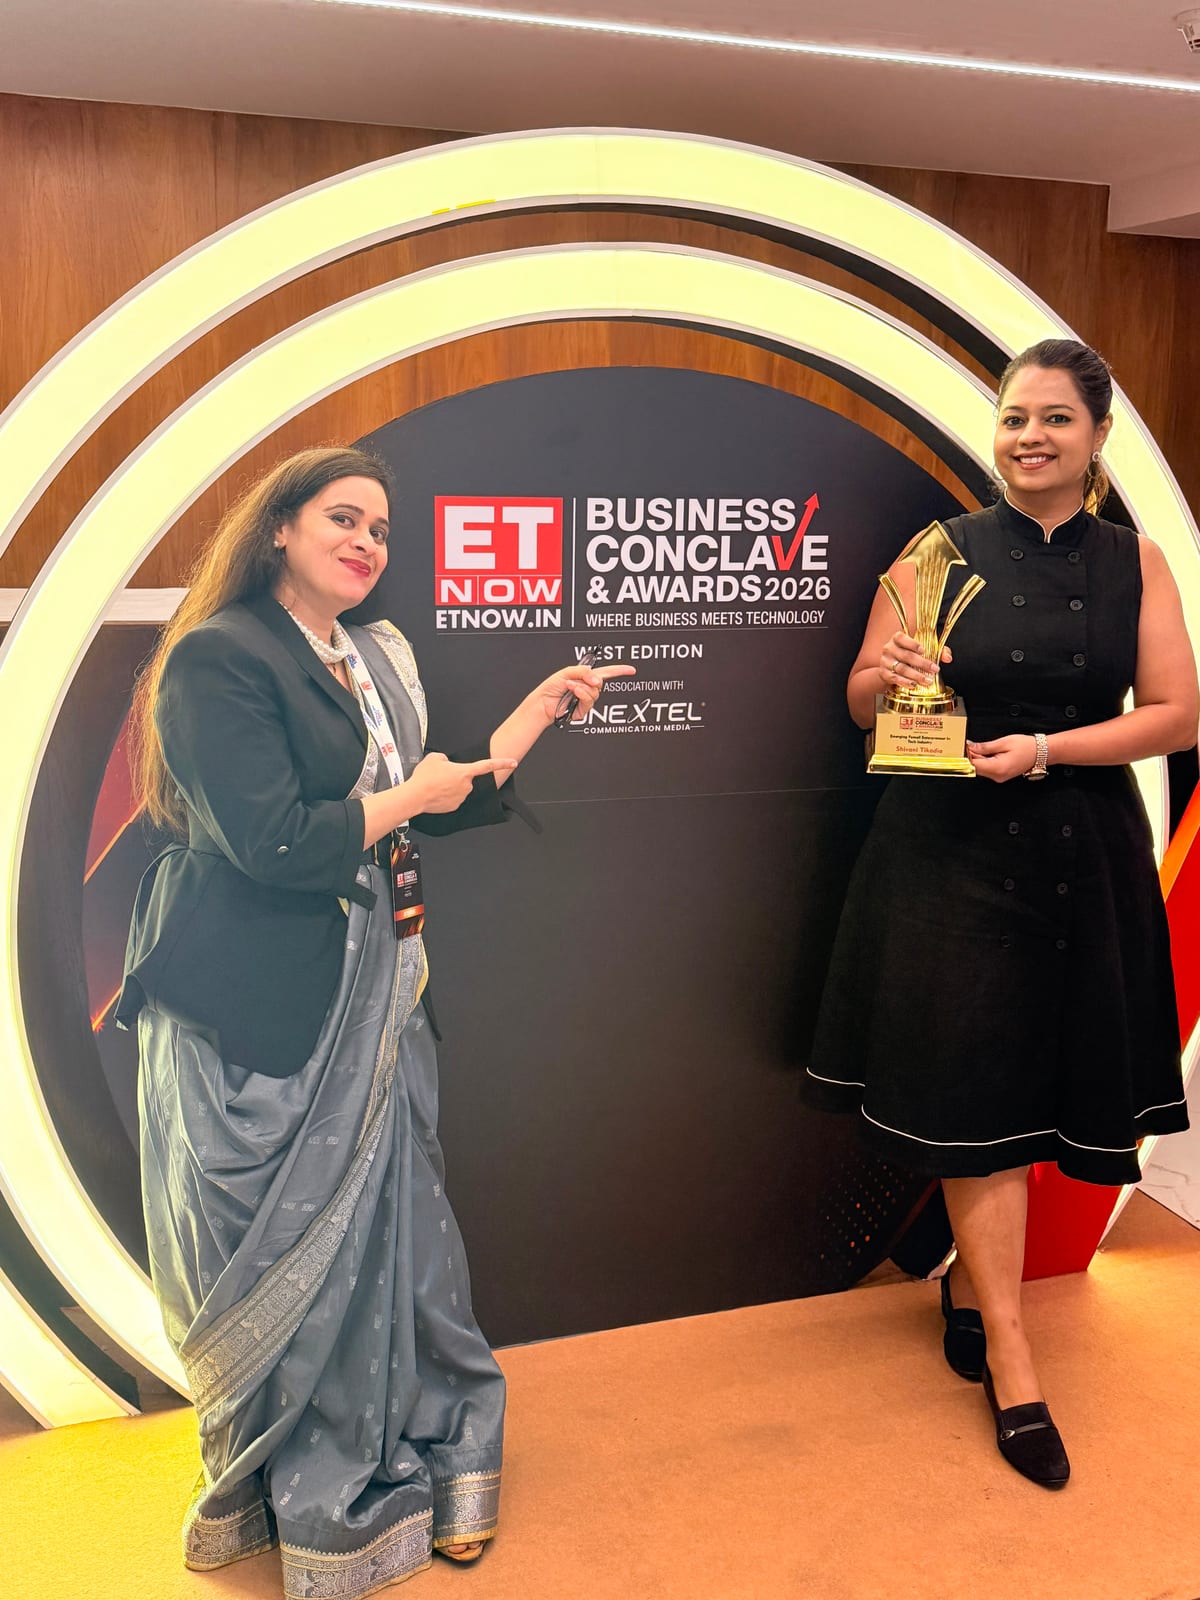
Recognition is a milestone, not the mission. Talk to our team about your security and compliance roadmap.
SecComply serves organisations across Dubai, Abu Dhabi, Sharjah, and the UAE free zones with one consistent security and compliance programme.
Regions served
Countries currently served
Hover, focus, or tap a marker to explore coverage.
Four regions. One accountable partner.
Four pillars, one partner, so nothing falls through the gaps between vendors.
Get strategic security leadership without a full time hire.
Bring on a virtual CISO who runs your security program day to day.
Helping security consultants scale their practice — we become your white-labelled delivery arm.
Build a security and compliance program that grows with your business, covering the frameworks you need, including ISO 27001, SOC 2, and GDPR.
Type I and Type II readiness and audit support, across the Trust Services Criteria your buyers ask for.
Structure the programme around Govern, Identify, Protect, Detect, Respond and Recover — and show where you stand.
Secure your applications through the full development lifecycle.
Find and fix risk across your cloud accounts and workloads.
Know what is in your software and vendor chain, and manage the risk you inherit.
Secure the AI you build and the AI you use, end to end.
Manage human, machine, and AI agent access before it becomes a blind spot.
A buyer questionnaire, contract clause, or investor deadline often starts the work. We build backwards from the date that matters.
Build the controls and evidence behind security questionnaires from banks, healthcare groups, and government linked entities.
Map one programme across a UAE entity, international delivery teams, and the frameworks your customers request.
Add a named vCISO who can own decisions, report to the board, and direct the delivery work.
Plan reviews, evidence collection, and audit support around the working hours of your UAE team.
We bring together the right technology, the right expertise, and the right processes to solve your security challenges—today and as your business grows.
We use AI-powered platforms to automate evidence collection, monitor risk, and simplify security operations.
Our AI agents automate repeatable security and compliance workflows—from evidence collection and control monitoring to follow-through—while experts retain approval, oversight, and accountability.
Tap into SecComply’s curated network of experienced cybersecurity specialists for hands-on implementation and strategic advisory—without building every capability in-house.
Solutions that help your business scale.
Everything you need to understand compliance, assess your readiness, and succeed in your journey.
Free 2-minute assessments to identify your ISO 27001, SOC 2, ISO 27701 and HIPAA readiness.
Run Assessment →Step-by-step guides for ISO 27001, SOC 2, and HIPAA certification, with timelines and best practices.
Read More →Pre-audit checklists and readiness assessments for every framework, so you prepare systematically.
Download →Latest insights on cybersecurity, compliance trends, and regulatory updates.
Read Blog →On-demand recordings of past webinars and upcoming live sessions with industry experts.
Watch →Protecting organizations in high-stakes, regulated sectors.
Payment security and audit readiness for regulated financial products.
Patient data protection and the controls auditors expect to see.
The certifications enterprise buyers ask for before they sign.
Cardholder data, customer privacy, and the platforms that carry both.
Hardened infrastructure and pipelines, assessed the way attackers would.
Governance for models and the identities they act through.
Programme-level governance across every business unit and vendor.
The shortest defensible path to your first certification.
“SecComply reduced our SOC 2 audit prep from 12 weeks to just 10 days. The automated evidence collection alone saved us hundreds of hours.”
“The AI risk assessment is game-changing. It identified compliance gaps we did not even know existed and gave us prioritized remediation steps.”
“Managing SOC 2, ISO 27001, and HIPAA simultaneously was impossible before SecComply. Now it is effortless with shared controls.”
Send us the questionnaire, contract clause, or customer request. We will tell you what it takes to get ready.